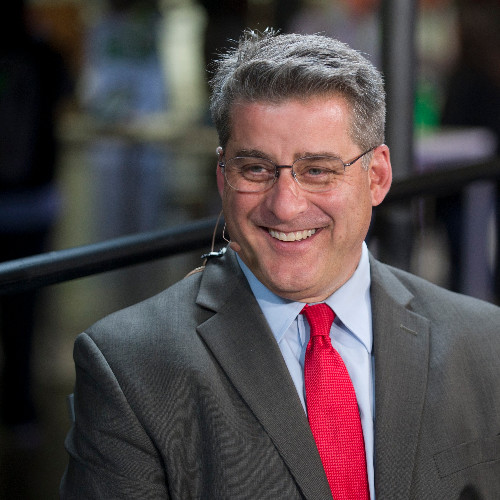
01. Tony Lee, FireEye, visits theCUBE ! (00:20)
02. Role of Technical Director at Mandiant/FireEye. (01:01)
03. Professional Services from a FireEye Perspective. (01:39)
04. Security Threat Use Cases. (02:14)
05. A Day in the Life of the Red Team. (03:59)
06. Where Splunk Fits in to Mandiant and FireEye. (06:22)
07. "You've Probably Already Been Compromised". (07:03)
08. Defining Malware. (08:48)
09. The "Vibe" at Splunk.conf. (09:43)
#theCUBE #Splunk #FireEye #Mandiant #SiliconANGLE
--- ---
Cyber security leader stays one step ahead of attackers | #splunkconf
by Heather Johnson | Sep 25, 2015
It’s more than a little unnerving for a big company to purposely experience an attack. But that’s just what FireEye, a cyber security leader, does when it “Red Teams” for clients.
“Red teaming is a valuable service for companies, because often they may not know what it’s really like to face the adversary,” Tony Lee, FireEye Inc.’s technical director of security consulting services, told Jeff Frick, cohost of theCUBE, from the SiliconANGLE Media team, during Splunk.conf 2015. “We show clients what it’s like to be specifically targeted. After seeing one attack and learning from mistakes, they are more ready to face the real world.”
Enabling event correlation
Lee said that Splunk is a great partner for FireEye because it augments FireEye data. “We want our data to be available for all of Splunk’s users, and it enables event correlation,” Lee stated.
Much of that data relates to some of the largest security breaches in the industry. “We are on the ground level,” said Lee. “We see things that nobody else sees. The attacker techniques and procedures are always evolving. We see new tools being integrated into hacks; in particular, WMI, PowerShell attacks. It’s ever evolving. We have to stay one step ahead of the attackers. We can apply our incident response knowledge to our proactive services to emulate the adversary because we see what they’re doing firsthand.”
@theCUBE
#splunkconf
Forgot Password
Almost there!
We just sent you a verification email. Please verify your account to gain access to
Splunk.conf 2015 | Las Vegas. If you don’t think you received an email check your
spam folder.
In order to sign in, enter the email address you used to registered for the event. Once completed, you will receive an email with a verification link. Open this link to automatically sign into the site.
Register For Splunk.conf 2015 | Las Vegas
Please fill out the information below. You will recieve an email with a verification link confirming your registration. Click the link to automatically sign into the site.
You’re almost there!
We just sent you a verification email. Please click the verification button in the email. Once your email address is verified, you will have full access to all event content for Splunk.conf 2015 | Las Vegas.
I want my badge and interests to be visible to all attendees.
Checking this box will display your presense on the attendees list, view your profile and allow other attendees to contact you via 1-1 chat. Read the Privacy Policy. At any time, you can choose to disable this preference.
Select your Interests!
add
Upload your photo
Uploading..
OR
Connect via Twitter
Connect via Linkedin
EDIT PASSWORD
Share
Forgot Password
Almost there!
We just sent you a verification email. Please verify your account to gain access to
Splunk.conf 2015 | Las Vegas. If you don’t think you received an email check your
spam folder.
In order to sign in, enter the email address you used to registered for the event. Once completed, you will receive an email with a verification link. Open this link to automatically sign into the site.
Sign in to gain access to Splunk.conf 2015 | Las Vegas
Please sign in with LinkedIn to continue to Splunk.conf 2015 | Las Vegas. Signing in with LinkedIn ensures a professional environment.
Are you sure you want to remove access rights for this user?
Details
Manage Access
email address
Community Invitation
Tony Lee, FireEye | Splunk .conf2015
01. Tony Lee, FireEye, visits theCUBE ! (00:20)
02. Role of Technical Director at Mandiant/FireEye. (01:01)
03. Professional Services from a FireEye Perspective. (01:39)
04. Security Threat Use Cases. (02:14)
05. A Day in the Life of the Red Team. (03:59)
06. Where Splunk Fits in to Mandiant and FireEye. (06:22)
07. "You've Probably Already Been Compromised". (07:03)
08. Defining Malware. (08:48)
09. The "Vibe" at Splunk.conf. (09:43)
#theCUBE #Splunk #FireEye #Mandiant #SiliconANGLE
--- ---
Cyber security leader stays one step ahead of attackers | #splunkconf
by Heather Johnson | Sep 25, 2015
It’s more than a little unnerving for a big company to purposely experience an attack. But that’s just what FireEye, a cyber security leader, does when it “Red Teams” for clients.
“Red teaming is a valuable service for companies, because often they may not know what it’s really like to face the adversary,” Tony Lee, FireEye Inc.’s technical director of security consulting services, told Jeff Frick, cohost of theCUBE, from the SiliconANGLE Media team, during Splunk.conf 2015. “We show clients what it’s like to be specifically targeted. After seeing one attack and learning from mistakes, they are more ready to face the real world.”
Enabling event correlation
Lee said that Splunk is a great partner for FireEye because it augments FireEye data. “We want our data to be available for all of Splunk’s users, and it enables event correlation,” Lee stated.
Much of that data relates to some of the largest security breaches in the industry. “We are on the ground level,” said Lee. “We see things that nobody else sees. The attacker techniques and procedures are always evolving. We see new tools being integrated into hacks; in particular, WMI, PowerShell attacks. It’s ever evolving. We have to stay one step ahead of the attackers. We can apply our incident response knowledge to our proactive services to emulate the adversary because we see what they’re doing firsthand.”
@theCUBE
#splunkconf